gogs.io/gogs
Affected
- introduced
0, fixed0.14.3(semver)
Fixed versions
0.14.3
Fix
- Fixed version
0.14.3go get gogs.io/[email protected]
Advisory
Also known as: CVE-2026-52796, GO-2026-5124
Gogs has DoS in rendering issue index pattern
Summary
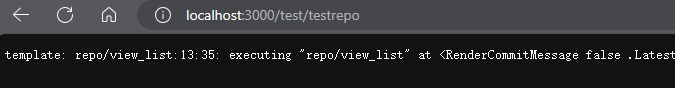
Special template of issue index pattern may cause panic.
Details
in internal/markup/markup.go
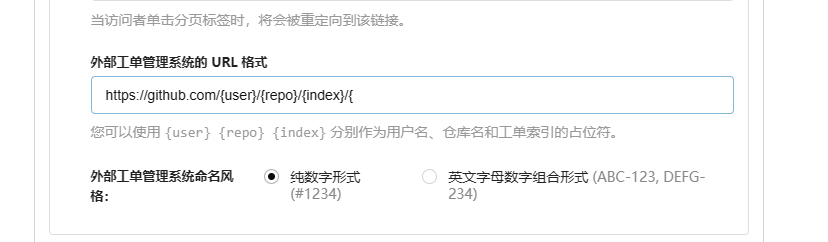
link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m)Issue index pattern is rendered to link with com.Expand.
However, com.Expand is not safe.
i = strings.Index(template, "}")
if s, ok := match[template[:i]]; ok {
when { is found but } not found, i comes to 1, template[:-1] will be called, and then panicked
finally, all pages than contains issue index are unavailable.
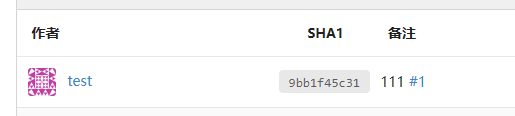
PoC
using #1 above
Impact
DoS that cause part of pages of the specify repo unavailable.
Low Basis: The source's own band: LOW
0, fixed 0.14.3 (semver)0.14.3
0.14.3go get gogs.io/[email protected]Fix commands are the export's own generic commands. Ojuju never runs them. Check them against your setup first.
Check your own computer: guard packages check
Source: GitHub Advisory Database (reviewed advisories) · CC BY 4.0