

uptime-kuma
Affected
- introduced
1.20.0, fixed1.23.7(semver)
Fixed versions
1.23.7
Fix
- Fixed version
1.23.7npm install [email protected]
Advisory
Also known as: CVE-2023-49276
Attribute Injection leading to XSS(Cross-Site-Scripting)
Summary
Google Analytics element Attribute Injection leading to XSS
Details
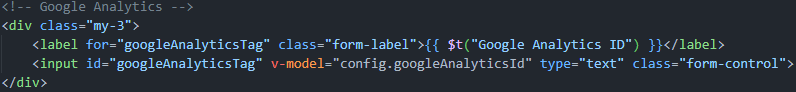
Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks.
image
PoC
123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="xscreenshots:
image
Medium Basis: The source's own band: MODERATE
1.20.0, fixed 1.23.7 (semver)1.23.7
1.23.7npm install [email protected]Fix commands are the export's own generic commands. Ojuju never runs them. Check them against your setup first.
Check your own computer: guard packages check
Source: GitHub Advisory Database (reviewed advisories) · CC BY 4.0